Storage Solutions are the systems and services that keep digital information available, protected, and usable. They include local drives, cloud platforms, network-attached storage, and hybrid environments. Each option handles data differently. Some store files on office hardware, while others distribute information across remote data centers.
David Hitz, co-founder of NetApp and a respected storage technology expert, once said, “The purpose of storage is to make data available when and where it is needed.” This idea remains central today. A storage solution receives data, organizes it, and retrieves it when applications or people request access. It may also create backups, copy information between locations, or reduce duplicate files. A warehouse offers a simple comparison. Shelves hold products, labels identify them, and workers locate orders quickly. Storage systems perform similar tasks with documents, databases, images, and business records.
The best choice depends on data volume, access speed, security needs, budget, and recovery goals. Solid-state storage can open files quickly. Cloud storage can expand without installing more equipment. However, convenience does not guarantee resilience. A poorly planned system may lose access during outages or make recovery painfully slow. Even experts must review assumptions. A solution that works for a small studio may fail under a hospital’s data load. This article examines how Storage Solutions operate, where their strengths appear, and which practical questions deserve attention before implementation.
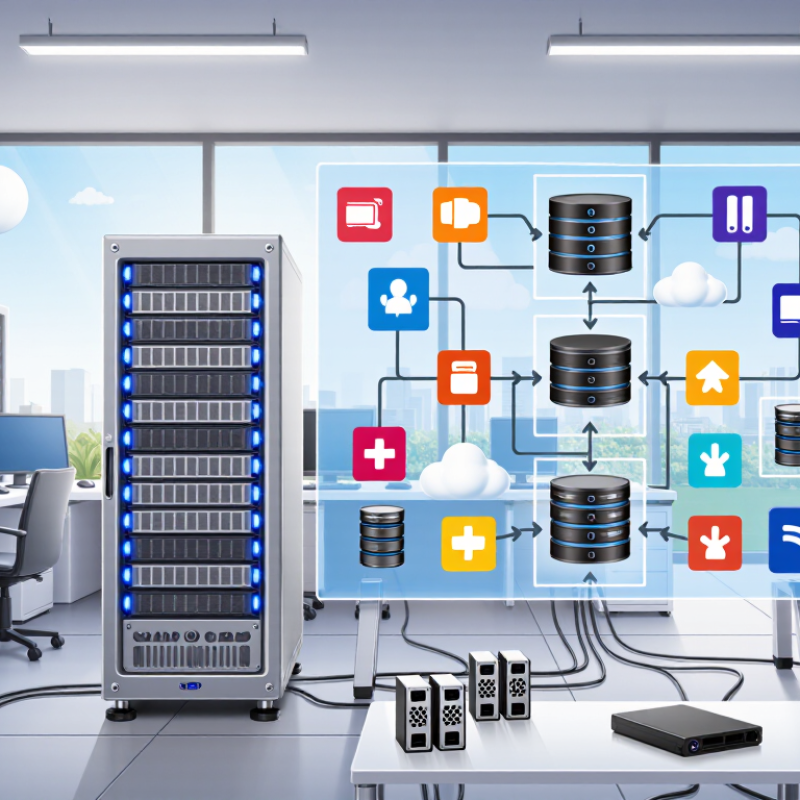
Storage solutions are organized methods for saving, retrieving, and protecting digital information. Their design determines how data moves, scales, and remains available during hardware failures. The main models are file, block, object, and cloud storage. Each solves a different operational problem, although real environments often combine them.
File storage arranges information in folders and filenames, much like documents in a cabinet. It suits shared workspaces where people need familiar navigation and controlled permissions. Block storage divides data into fixed sections that servers can access independently. Databases often prefer it. This model supports consistent performance, but administrators must manage formatting, allocation, and recovery carefully. Object storage keeps each item with descriptive metadata and a unique identifier. That structure works well for images, backups, logs, and large archives. The boundary is not always clean.
Cloud storage is a delivery model, not always a separate data structure. It can provide file, block, or object services through remote infrastructure. Capacity may expand quickly, but costs can rise through access, transfer, or retention charges. Network delays matter. Reliable planning includes encryption, identity controls, versioning, and tested recovery procedures. Teams should measure actual workloads instead of trusting default settings. That lesson is easy to miss. A fast system may still fail when permissions, monitoring, or recovery ownership remain unclear.
Storage solutions preserve data and make it available when applications request it. A hard disk drive stores bits on spinning magnetic platters. Its moving head creates noticeable seek delays, especially during scattered reads. A solid-state drive uses flash memory instead. It has no moving parts, so access is quieter and faster. NVMe storage uses a streamlined protocol over a high-speed bus. This reduces communication overhead and supports many parallel requests.
Tips: Match storage to the workload. HDDs can suit archives and large, sequential files. SSDs usually improve boot times, databases, and frequent file access. NVMe can help demanding analytics, virtual machines, and development tasks. However, faster hardware does not fix poor application design. I have seen systems with excellent drives remain slow because of inefficient queries and limited memory.
Data I/O performance depends on more than advertised speed. Latency measures how quickly one request begins to return. Throughput measures the volume transferred over time. Random I/O stresses storage differently from sequential I/O. Queue depth can improve parallel work, but excessive queues may increase waiting. Temperature, drive capacity, file-system settings, and workload patterns also matter. Results can look impressive in tests, yet feel ordinary in daily use. Measure real read and write behavior before choosing a solution.屣
Storage solutions keep data on disks, flash devices, or cloud-backed systems. Their real test begins when hardware fails. An annualized HDD failure rate of 1.7% sounds small, but it changes risk calculations. In a rack holding 1,000 drives, simple multiplication suggests about 17 failures yearly. That estimate is not a promise. Age, workload, temperature, and drive batches can shift the result.
RAID spreads data across multiple drives to preserve access after a disk fault. RAID 1 mirrors data, while parity-based layouts use capacity more efficiently. During a rebuild, however, surviving drives work harder and may expose another weakness. A hot spare can shorten this window. It cannot remove the danger. Teams sometimes treat RAID as backup, which is a costly misunderstanding. RAID protects availability, not deleted or corrupted files.
Replication creates additional copies across separate failure domains. A second server in the same room helps with disk failure, but not fire, flooding, or power loss. Cross-site copies reduce those risks, provided they are tested. Recovery drills should measure restore time, missing permissions, and application consistency. Monitoring should track failed sectors, rebuild speed, latency, and backup age. One uncomfortable lesson remains: redundancy can look impressive while hiding weak recovery procedures.
Storage solutions organize digital files so applications can save, retrieve, protect, and scale data. Object storage treats each file as an independent object with content, metadata, and a unique identifier. This design suits photographs, backups, logs, and large media files.
The eleven-nines durability model promises 99.999999999% durability for stored objects. In simple terms, the expected risk is losing one object among 100 billion during a year. This result comes from distributing data across separate facilities, checking data integrity, and rebuilding damaged copies automatically. Erasure coding can also protect information without keeping identical copies everywhere.
Small details matter here. A checksum may detect a silent bit error before it spreads.
Durability is not the same as availability. A durable object may remain intact while a service interruption prevents access. The model also cannot stop an authorized user from deleting data or uploading a damaged file. Versioning, access controls, retention policies, and tested recovery procedures remain essential. In practice, teams should examine real restore times, not only impressive percentages. A monthly recovery drill can expose missing permissions, unclear ownership, or an overlooked dependency. Eleven nines sounds nearly perfect, but it describes a statistical design target, not a promise against every human mistake.
Storage solutions combine physical media, cloud repositories, and software that organizes growing amounts of information. Their real value appears during failure. A damaged laptop, accidental deletion, or power outage can interrupt daily work within minutes. Reliable storage requires more than capacity; it requires controlled protection and recovery procedures.
The 3-2-1 backup rule provides a practical foundation: keep three copies of important data, on two different media types, with one copy stored off-site. For example, active files may remain on a local server, a second copy on separate backup media, and a third in a protected remote location. Test restores regularly. A backup that cannot be restored is only a comforting assumption. Short tests matter.
Encryption protects information while stored and while moving between systems. Strong access controls should protect the encryption keys, because encrypted files are not useful if keys are lost. Lifecycle policies add discipline by defining when data is created, retained, archived, or securely deleted. A project folder might stay active for one year, then move to lower-cost storage. Sensitive records may require longer retention. Rules must reflect business needs and applicable requirements. They should also be reviewed when operations change. Policies often look perfect on paper. People still mislabel files, skip tests, or keep unnecessary copies. That weakness deserves regular review.
A practical comparison of storage methods and data-protection controls
| Storage or Control | How It Works | Best-Fit Use | Key Strength | Primary Limitation | Protection Considerations |
|---|---|---|---|---|---|
| Direct-Attached Storage (DAS) | Storage devices connect directly to one computer or server through a local interface. | Individual workstations, small servers, and local high-speed file access. | Low latency and straightforward deployment. | Usually has limited sharing and may create a single point of failure. | Use separate backups, access controls, disk monitoring, and encryption where sensitive data is stored. |
| Network-Attached Storage (NAS) | A dedicated device provides shared files over a local network using file-based protocols. | Team collaboration, shared documents, and centralized departmental files. | Centralized access with permissions and shared-folder management. | Network outages, device failure, or ransomware can affect shared access. | Configure user permissions, snapshots, immutable or offline backups, and encrypted network connections. |
| Storage Area Network (SAN) | A specialized network presents block storage to servers, often for databases and virtual machines. | Enterprise workloads requiring high performance and centralized storage management. | Consistent performance, scalability, and advanced availability features. | Higher cost, operational complexity, and specialized administration requirements. | Separate storage redundancy from backup, restrict administrative access, and test recovery procedures. |
| Object Storage | Data is stored as objects with content, metadata, and a unique identifier, commonly accessed through APIs. | Unstructured data, archives, media, logs, and large-scale analytical datasets. | High durability potential, elastic capacity, and rich metadata support. | Not ideal for every low-latency or traditional file-system workload. | Enable versioning, access logging, retention controls, encryption, and protection against unauthorized deletion. |
| Cloud Storage | Storage capacity is delivered over a network and managed through provider-controlled infrastructure and service interfaces. | Flexible capacity, remote access, backup repositories, and distributed applications. | Rapid scaling without purchasing and maintaining all physical equipment. | Costs, performance, availability, and data location depend on configuration and connectivity. | Review shared-responsibility duties, apply least privilege, encrypt data, and monitor access and spending. |
| 3-2-1 Backup Strategy | Maintain at least three copies of data, on two different storage media or systems, with at least one copy off-site. | Reducing exposure to hardware failure, human error, malware, and site-level incidents. | Creates multiple recovery paths instead of relying on one storage system. | It is a planning framework, not a guarantee; copies must still be monitored and tested. | Use an offline or immutable copy when possible, define recovery objectives, and perform documented restore tests. |
| Encryption at Rest | Data is cryptographically protected while stored on disks, databases, removable media, or backup repositories. | Sensitive personal, financial, operational, and confidential information. | Reduces the usefulness of stolen or improperly accessed storage media. | Lost keys, weak key access controls, or unencrypted copies can undermine protection. | Protect keys separately, limit key access, rotate keys according to risk, and verify that backups are also encrypted. |
| Encryption in Transit | Data is encrypted while moving between users, systems, networks, or storage services. | File transfers, remote administration, application traffic, and backup replication. | Helps prevent interception or alteration during transmission. | Does not protect data after it reaches an exposed endpoint or improperly secured destination. | Use authenticated secure protocols, certificate validation, and endpoint security controls. |
| Lifecycle Policy | Rules define how data is created, classified, accessed, retained, archived, and securely deleted. | Managing cost, compliance obligations, retention periods, and information sprawl. | Aligns storage location and cost with the data’s business value and access frequency. | Incorrect retention rules can cause premature deletion or unnecessary storage expense. | Document owners and retention periods, apply legal holds where required, and securely dispose of expired data. |
1 Hayotsrim Street
Nahariya 22311
Israel
Phone: +972 (0)4 9855 121/ 111/ 176
Fax: +972 (0)4 9855 175
Email: sale@dialoguetoolkit.com
Url: www.egmo.co.il
1 Hayotsrim Street
Nahariya 22311
Israel
Phone: +972 (0)4 9855 121/ 111/ 176
Fax: +972 (0)4 9855 175
Email: sale@dialoguetoolkit.com
Url: www.egmo.co.il
An der Autobahn 15
D-28876 Oyten
Germany
Phone: +49 4207 699 40
Fax: +49 4207 6994 40
E-mail: sale@dialoguetoolkit.com
Url: www.hy-lok.de
Distributor in Belgium
Avenue Lavoisier 18B
1300 Wavre
Belgium
Phone: +32(0)471 93 43 12
Email: sale@dialoguetoolkit.com
Url: www.cameco-tubings.be
Distributor in Belgium Flanders
Steenspil 8
4661 TZ Halsteren
The Netherlands
Phone: +31(0)85 0074200
E-mail: sale@dialoguetoolkit.com
Url: www.bergen-ip.eu
Sklarska 70
435 42Litvinov
Czech Republic
Phone: +420 602 110 208
Email: sale@dialoguetoolkit.com
Url: www.hacomost.cz
Rusthollarinkatu 8
Espoo FIN-02270
Finland
Phone: +358 (0) 106137100
Fax: +358 (0) 106137701
Email: sale@dialoguetoolkit.com
Url: www.avs-yhtiot.fi
ZI du Val d’Argent
11 rue Guy Moquet
95100 Argenteuil
France
Phone: +33 1 30 25 94 20
Fax: +33 1 30 25 94 59
Email: sale@dialoguetoolkit.com
Url: defa-inox.fr
An der Autobahn 15
Oyten D-28876
Germany
Phone: +49 – 4207 – 69 94 – 0
Fax: +49 – 4207 – 69 94 – 40
Email: sale@dialoguetoolkit.com
Url: www.hy-lok.de
Skouze 14
Piraeus 18536
Greece
Phone: +30 (0)210-4530240
Email: sale@dialoguetoolkit.com
Url: www.agv.gr
Via Novara 10 / B-C
20013 Magenta
Milano
Italy
Phone: +39 02 97298663
Fax: +39 02 97291855
Email: sale@dialoguetoolkit.com
Url: www.indra.it
Distributor for Lithuania, Estonia & Latvia
Serveces g. 2-27
02121 Vilnius
Lithuania
Phone: +370 (5) 210 22 74
Fax: 370 (5) 210 22 75
Email: sale@dialoguetoolkit.com
Url: tekknow.lt
Distributor for Israel, Moldova, Kosovo, Iceland, Hungary, Slovenia, Romania, Bulgaria & Malta
Buitenvaart 1411
Hoogeveen 7905 SJ
The Netherlands
Phone: +31(0)528 234 084
Fax: +31(0)528 234 084
Email: sale@dialoguetoolkit.com
Url: www.www.dialoguetoolkit.com
Bijsterhuizen 2152
6604 LG Wijchen
the Netherlands
Phone: +31 (0)24 648 93 80
E-mail: sale@dialoguetoolkit.com
Url: www.pdgastechnology.nl
Steenspil 8
4661 TZ Halsteren
The Netherlands
Phone: +31(0)85 0074200
E-mail: sale@dialoguetoolkit.com
Url: www.bergen-ip.eu
Energieweg 14
4691SG Tholen
The Netherlands
Phone: +31(0)85 0074200
E-mail: sale@dialoguetoolkit.com
Url: www.bergen-ip.eu
Strandgata 15A
4307 Sandnes
Phone: +47 91135785
Email: sale@dialoguetoolkit.com
Url: hydraserv.no
ul. Zalogowa 17
Gdansk 80-557
Poland
Phone: +48 58 522 03 80, -81
Fax: +48 58 342 20 10
Email: sale@dialoguetoolkit.com
Url: www.verdigroup.pl
Estrada Nacional 10
Centro Empresarial SADO
Internacional Armazem C 19
2910-809 Setúbal
Portugal
Phone: +351 919 582643
Email: sale@dialoguetoolkit.com
Url: www.arcamo.com
Distributor for Serbia, Croatia, Bosnia & Herzegovina, Montenegro, North Macedonia & Albania
Cara Dusana 205A
11080 Belgrade
Serbia
Phone: +381 60 46 56 086
Email: sale@dialoguetoolkit.com
Url: www.timfluid.com
Partizánska Ľupča 552
032 15 Partizánska Ľupča
Slovak Republic
Phone: +421 903 735 360
Email: sale@dialoguetoolkit.com
Url: www.ecmsystems.sk
C/ Sebastián Elcano 32, 2ª Planta, Puerta 33
28012 Madrid
Spain
Phone: +34 916 794 286
Fax: +34 916 794 287
Email: sale@dialoguetoolkit.com
Url: www.arcamo.com
Distributor for Sweden, Denmark & Faroe Islands
Metalgangen 13
2690 Karlslunde
Denmark
Phone: +45 7384 1230
Fax: +45 7384 1280
Email: sale@dialoguetoolkit.com
Url: pgflowteknik.dk
Distributor for Sweden, Denmark & Faroe Islands
Metalgangen 13
2690 Karlslunde
Denmark
Phone: +45 7384 1230
Fax: +45 7384 1280
Email: sale@dialoguetoolkit.com
Url: pgflowteknik.dk
An der Autobahn 15
D-28876 Oyten
Germany
Phone: +49 4207 699 40
Fax: +49 4207 6994 40
E-mail: sale@dialoguetoolkit.com
Url: www.hy-lok.de
Neumo Mühendislik ve Paslanmaz Çelik San. Tic. Ltd. Şti.
Birlik sanayi Sitesi 6. Cadde No:19
34520 Beylikdüzü/Istanbul
Turkey
Phone: +90 (212) 875 01 41
Fax: +90 (212) 875 23 13
Email: sale@dialoguetoolkit.com
Url: www.neumo.com.tr/
Kirkhill Place
Kirkhill Industrial Estate
Dyce AB21 0GU
United Kingdom
Phone: +44 (0) 1224 775277
Fax: +44 (0) 1224 775040
Email: sale@dialoguetoolkit.com
Url: www.hylokuk.com
ST. Semenovskaya B., D49, APT/FLOOR/OFFICE I/5/16
107023 MOSCOW
RUSSIA
Phone: +7 495 517 7261
Fax: +7 495 360 8062
Email: sale@dialoguetoolkit.com
Url: www.fluid-line.ru